This website uses cookies. By clicking Accept, you consent to the use of cookies. Click Here to learn more about how we use cookies.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Extreme Networks
- Community List
- Switching & Routing
- ExtremeSwitching (EXOS/Switch Engine)
- EXOS Packet Capture
Options
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark
- Subscribe
- Mute
- Printer Friendly Page
EXOS Packet Capture
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
05-18-2021 01:00 PM
Hello,
today I played around with the built-in packet capture of EXOS ( How To: How to perform a local packet capture on an EXOS switch | Extreme Portal (force.com) )
I’m able to capture packets and open the pcap file with wireshark, but I only see the following packets:
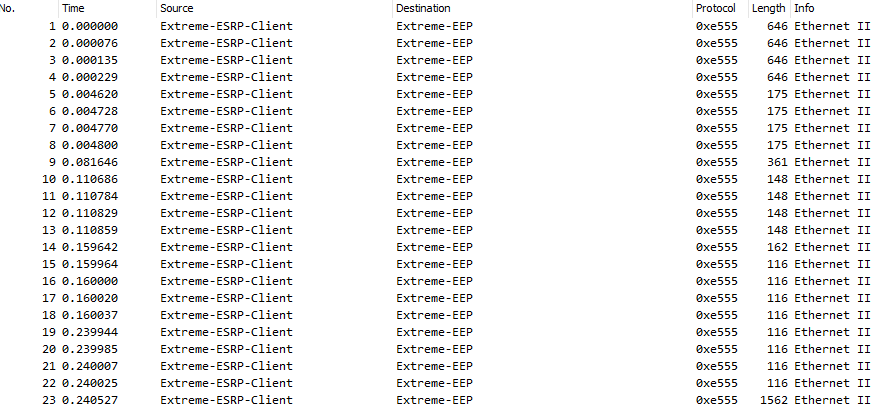
Wondering if I’m doing something wrong or if the feature is something else than I’m thinking. Any hints?
Best regards
Stefan
Solved! Go to Solution.
2 ACCEPTED SOLUTIONS
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
05-18-2021 03:54 PM
Hi,
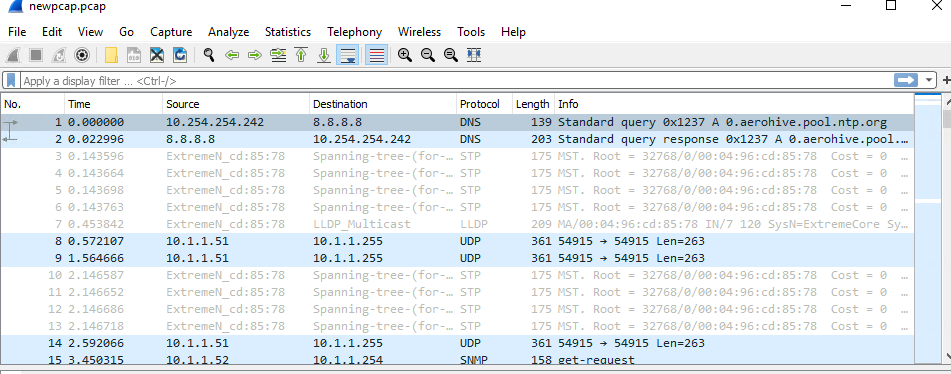
You can use the editcap tool to remove the first 52 bytes. Mine looked something like below from Powershell:
PS C:\Program Files\Wireshark> .\editcap.exe -C 52 editcap.pcap newpcap.pcap

syntax below:
PS C:\Program Files\Wireshark> .\editcap.exe -C 52 <original pcap filename> <new pcap filename>
Below is more on editcap:
https://www.wireshark.org/docs/man-pages/editcap.html
Before:
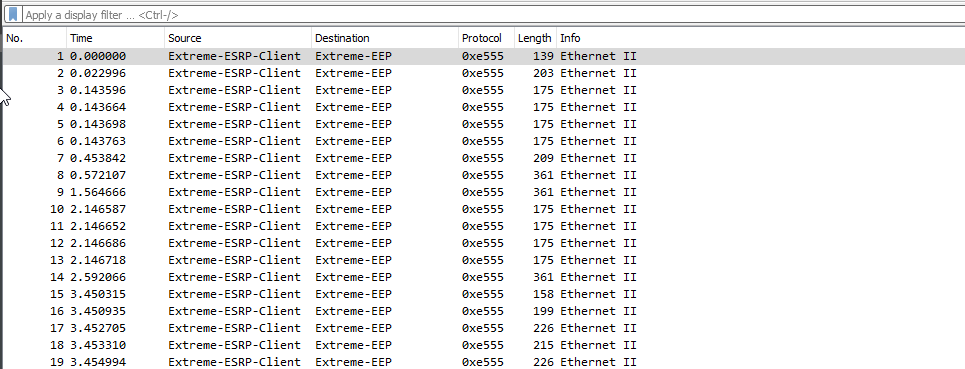
After:
Thanks,
Chris Thompson
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
07-21-2026 09:42 PM - edited 07-21-2026 09:43 PM
This is an interesting question because the built-in packet capture feature can be a bit confusing at first. If you're only seeing those packets in Wireshark, it may be related to the capture point, applied filters, or hardware offloading rather than the traffic itself. Checking the interface configuration and testing with a known traffic Gomovies flow could help narrow down the cause. I'd be interested to know what the final solution was, as it could be useful for anyone troubleshooting EXOS packet captures in the future.
23 REPLIES 23
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
Tuesday - last edited Tuesday
Interesting discussion! EXOS built-in packet capture seems like a convenient way to troubleshoot network issues without needing additional hardware. However, seeing only a limited number of packets in Wireshark can make it difficult to identify the actual problem. It would be helpful to understand the capture filters and interface settings to ensure the required traffic is being recorded correctly. https://f2movies.se/
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
a week ago - last edited a week ago
Great discussion about EXOS packet capture! Being able to capture traffic directly from the switch and analyze it in Wireshark is really useful for troubleshooting network issues. If only a limited set of packets appears in the capture, it would be interesting to check the capture filters, selected ports, and whether the desired traffic is actually passing through the monitored interface. Understanding these details can make packet analysis much more effective. https://dorawatch.us/
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
a week ago - last edited a week ago
This is a really interesting look at the built-in packet capture capabilities of EXOS. Being able to collect traffic directly from the switch and then inspect the resulting PCAP 24Drama in Wireshark is extremely useful for troubleshooting. However, seeing only a limited set of packets can definitely raise questions about the capture configuration, filters, or which traffic the switch is actually exposing. It would be great to see what settings were used and what needs to be adjusted to capture the expected traffic.
Options
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Get Direct Link
- Report Inappropriate Content
2 weeks ago
Interesting! The built-in packet capture feature in EXOS seems useful for troubleshooting network issues. If Wireshark is only showing a limited set of packets, it would be worth checking the capture filters, interface configuration, and whether the traffic you want to analyze is actually passing through the monitored port. Hopefully, a few adjustments will help reveal the missing traffic and make the packet analysis more useful. https://brocoflix.watch/

